
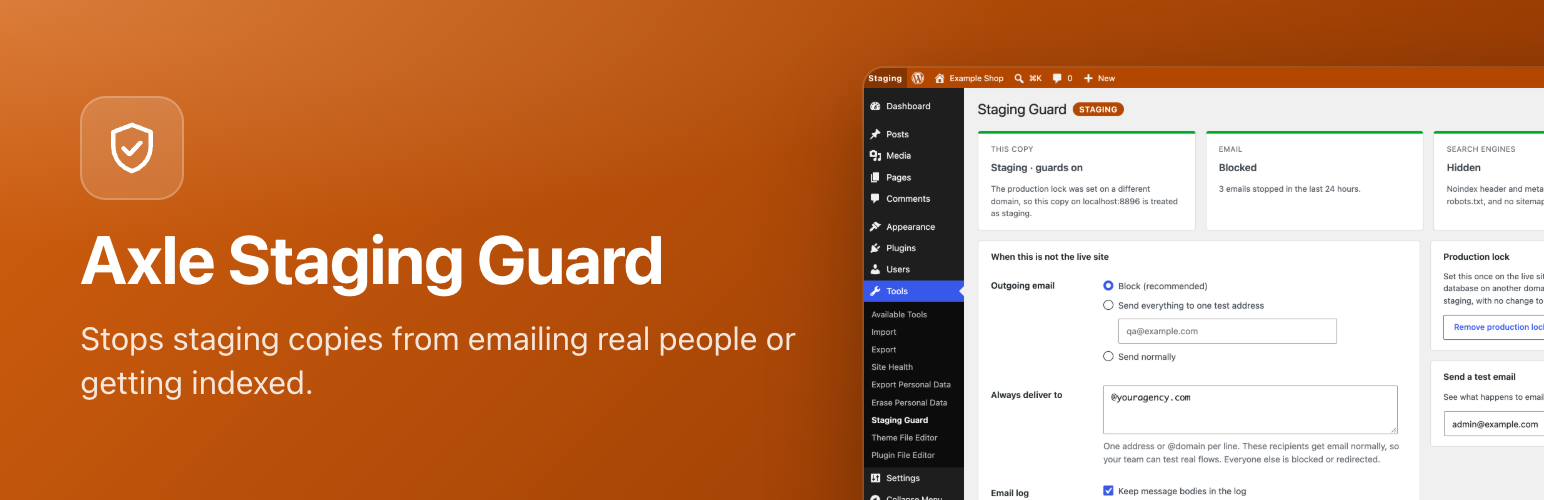

Description
Every agency has a staging story. A copy of the live database goes to staging, and then:
- a scheduled task emails every customer from the staging site,
- Google indexes staging.example.com and it outranks the real site,
- someone spends an hour editing staging, thinking it was live.
A fourth one is quieter: the copy keeps talking to your payment gateway, CRM, Mailchimp list or Zapier webhooks with the live keys it inherited.
Axle Staging Guard prevents all four, on every copy that is not the live site.
On staging, development and local copies it:
- Blocks all outgoing email, or sends it all to one test address with the real recipients shown in the subject. Cc and Bcc recipients are removed too.
- Lets your own team keep receiving email: list addresses or whole domains (@youragency.com) under “Always deliver to”.
- Keeps a list of the last 50 stopped emails (recipient, subject and time), so you can see what would have gone out. Turn on “keep message bodies” to check email content as well.
- Sends a test email from the settings screen, so you can see exactly what happens to email from this copy.
- Blocks outgoing API calls except to hosts you allow, or just logs them. It covers requests made through the WordPress HTTP API, which is what payment gateways, CRM and marketing plugins, webhook plugins, Slack notifications and license checks use. A blocked call fails with a clear error, never a fake success.
- Always lets through what WordPress needs: wordpress.org and its subdomains (updates, translations, the plugin directory), the site’s own address and localhost. Add your own hosts, with wildcards like
*.example.com. - Keeps a list of the stopped or logged calls: method, host, path, the plugin that made them and how often. No query strings, bodies or headers, and keys in webhook URLs are masked.
- “Test a URL” shows what would happen to a request, without sending it.
- Hides the site from search engines with an
X-Robots-Tagheader, anoindex, nofollowrobots meta tag and a robots.txt that blocks everything, and turns off the XML sitemap. - Colours the whole admin bar (orange for staging, blue for development, green for local) and labels it, on the dashboard and on the front end.
- Adds the environment to every browser tab title, for example “[Staging] Posts”, so the right tab is easy to find.
- Adds a Site Health check that warns when email from a staging copy could still reach real people, or when staging copies of the live site would not be detected.
On the live site it does nothing.
Free and open source under the GPL. No pro version, no upsells, no ads in wp-admin, no tracking. And it stays that way.
Part of Axle by AryanX, a family of free plugins for running WordPress sites safely.
How it knows which copy is live
- If
WP_ENVIRONMENT_TYPEis set in wp-config.php or in the server environment, it uses that. This is the WordPress standard, and many hosts set it for you. - Otherwise, use the production lock: on the live site, go to Tools > Staging Guard and click “This is the live site”. From then on, any copy of the database running on a different domain is treated as staging, with no wp-config.php change.
The lock stores a hash of the live domain instead of the domain itself. Migration tools that search and replace the domain name in the database leave the hash alone, so the lock survives the copy to staging.
If neither is set, WordPress assumes production and Axle Staging Guard stays off.
Settings in wp-config.php
Fix the email behaviour per environment, so a database copy cannot change it:
define( 'AXLE_STAGING_GUARD_MAIL_MODE', 'redirect' ); // block, redirect or allow
define( 'AXLE_STAGING_GUARD_REDIRECT_TO', 'qa@example.com' );
define( 'AXLE_STAGING_GUARD_ALLOWLIST', '@youragency.com, client@example.com' );
define( 'AXLE_STAGING_GUARD_HTTP_MODE', 'block' ); // allow, log or block
define( 'AXLE_STAGING_GUARD_HTTP_ALLOWED_HOSTS', 'sandbox.paypal.com, *.youragency.com' );
define( 'AXLE_STAGING_GUARD_HTTP_BLOCKED_HOSTS', 'hooks.slack.com' ); // always blocked, in every mode
define( 'AXLE_STAGING_GUARD_PRODUCTION_HOSTS', 'example.com, shop.example.com' ); // the live domains
define( 'AXLE_STAGING_GUARD_KEEP_BODIES', false );
define( 'AXLE_STAGING_GUARD_NOINDEX', true );
define( 'AXLE_STAGING_GUARD_LOG_DAYS', 7 );
WP-CLI
wp axle-staging-guard statusshows the environment, how it was detected, and what is guarded.wp axle-staging-guard lock-productionmarks the current domain as the live site.wp axle-staging-guard unlock-productionremoves the lock.wp axle-staging-guard loglists stopped email.wp axle-staging-guard test-email you@example.comsends a test email and reports what happened to it.wp axle-staging-guard http-loglists blocked and logged outgoing requests.wp axle-staging-guard test-url https://api.example.com/v1says what would happen to a request to that URL.
Try it before you install. try.axlewp.com/axle-staging-guard opens a private WordPress in your browser with this plugin and some demo content.
FAQ
Does it work with SMTP plugins?
Yes, for plugins that send through WordPress’s own wp_mail() function, which is most of them. A few plugins replace wp_mail() entirely. Axle Staging Guard detects this and shows a warning on its settings screen, because it cannot intercept those emails.
Will blocked emails break password resets on staging?
No. Blocked emails are reported to WordPress as sent, so forms and password resets behave normally. Use redirect mode if you need to receive them.
What if I copy the staging database to production?
The production lock is still stored, and the live domain still matches it, so the live site stays unguarded. The search engine setting under Settings > Reading is never changed by this plugin.
Can I change how the environment is detected?
Use the axle_staging_guard_environment filter. It receives an array with type (production, staging, development or local) and source.
What if the live site moves to a new domain?
Then the production lock no longer matches, and the live site would count as staging. Axle Staging Guard warns about this on every admin screen and in Site Health, so it does not go unnoticed. Lock the new domain from Tools > Staging Guard, or list every live domain in AXLE_STAGING_GUARD_PRODUCTION_HOSTS so a move never trips it. www. and the bare domain already count as the same.
Does the email log keep personal data?
The list of outgoing requests holds none: no query strings, bodies or headers, and parts of a path that look like email addresses, hashes or keys are hidden. The email log keeps who an email was for and its subject, and the message only if you turn that on. Entries are deleted after 7 days, and the email log is part of the WordPress export and erase personal data tools. The live site keeps no log.
Does it block my payment gateway’s test mode?
It blocks hosts, not modes. api.stripe.com and api.paypal.com are the same host whether the key is a test key or a live one, so in “Block all except allowed hosts” both are blocked until you allow them. Allow the sandbox host you want to test against (for example sandbox.paypal.com), or allow api.stripe.com only when the copy has test keys. Not sure which hosts a plugin calls? Use “Log only” for a day and read the list.
How do I allow a host?
Add it under Tools > Staging Guard > “Calls to other services” > Allowed hosts, one per line. api.example.com allows that host, and *.example.com allows every subdomain (but not example.com itself). You can also set AXLE_STAGING_GUARD_HTTP_ALLOWED_HOSTS in wp-config.php, or use the axle_staging_guard_http_allowed_hosts filter. “Test a URL” on the same screen shows whether an address would get through.
Does it affect production?
No. On the live site requests are never blocked, changed or recorded, whatever the settings say, and there is no list.
Will updating break my staging site?
No. Sites that already use the plugin keep “Allow all” for outgoing requests, so nothing changes until you choose. A fresh install starts on “Log only”, which lets everything through and records it, so you can see what the site calls before you start blocking. Site Health reminds you while a staging copy allows all calls.
What does a blocked request look like to the plugin that made it?
A failed request, like a network error: the WordPress HTTP API returns a WP_Error with the code axle_staging_guard_http_blocked. It is never reported as a success.
What does it not catch?
Code that does not go through the WordPress HTTP API: a PHP SDK that opens its own cURL connection, file_get_contents() on a URL, and anything the visitor’s browser sends (analytics scripts, embeds). Server-side requests from WordPress and from plugins that use wp_remote_get() and friends are covered.
Screenshots


Changelog
2.1.0
- New: guard outgoing API calls on staging, not only email
2.0.1
- Fix: label the Tools menu item “Staging Guard”
2.0.0
- Changed (breaking change): rename to Axle Staging Guard for WordPress.org
1.3.0
- Fix: make the abilities visible to MCP agents
- New: add abilities so AI agents can tell staging from the live site before doing anything risky
1.2.0
- New: add filters for email handling, robots.txt, colours and labels, and actions for the production lock
- Fix: warn when the live site counts as staging, and move the email log out of one option
1.1.0
- New: “Always deliver to” allowlist for addresses and @domains.
- New: send a test email from the settings screen or WP-CLI.
- New: optionally keep message bodies in the email log.
- New: Site Health check.
- New: environment shown in browser tab titles.
- New: redesigned settings screen with status cards.
- Rewritten as PSR-4 classes.
1.0.0
- First release.