


Description
DT-PM Consent is a privacy-first consent management plugin: you keep full
control over what is blocked, with no usage limits, no paywalls and no
external tracking.
Many consent tools lock essential features behind monthly tiers, or start
charging once your traffic grows. This one is free and fully functional from
day one. No pageview limits, no domain caps, nothing held back for a paid
tier, and no calls to a server of ours.
Why choose DT-PM Consent
- Truly unlimited. No pageview caps, no subscription, and no fee that
jumps when your site grows. Everything you need in order to be compliant is
in this plugin. - Strict pre-consent blocking. For the services you list, registered
scripts, the inline snippets attached to them, and embedded iframes of known
providers are rewritten into inert placeholders until consent is given. - Guided setup in four steps, with a scanner in two parts. A server-side
reader looks at what WordPress knows about; a collector records what
actually loads in your own browser, so a script injected at runtime is found
as well. - Local and private. The plugin contacts no external server at all. No
visitor log, no stored IP address, no identifier of any kind. - Fair by design. “Accept all” and “Reject all” carry the same weight on
the first level. No hidden reject button, no dark pattern. - A cookie declaration that stays current. A shortcode or a block, built
from the same data as the banner, so the two cannot end up saying different
things. - An evidence archive, exportable as CSV. Every configuration change is
recorded – what your banner said and when – without tracking individuals.
What it does not do (by design)
- No automatic guesswork. It does not blindly block scripts by guessing.
You keep full control over what gets blocked, so nothing breaks your theme
behind your back. - No external server calls. The plugin never sends data to any server of
ours – not on a schedule, not at all.
What exactly it can block, and what it can find but not stop, is answered
under Frequently Asked Questions.
Is there a paid version?
Yes – DT-PM Consent Plus, and we would of course like to sell it. You do not
need it to run this plugin, and you do not need it to meet your obligations –
everything required for that is here.
What it adds is work it takes off you. This plugin scans when you ask it to;
Plus watches on a schedule and tells you when something new turns up. This
plugin leaves the banner’s looks to your own CSS; Plus has fields for it. This
plugin is set up per site; Plus keeps several sites in one place.
You can run it for three months without paying. You need a free account at
dt-pm.eu to download it, but no payment and no card. Install it next to this
plugin and press the button that starts the free period – once per domain, and
only when a human presses it.
When the three months are over, it falls back to what this plugin does on its
own. Nothing you configured is lost and nothing of this plugin stops working –
Plus never replaces the free edition, it only adds to it.
This plugin shows one thing for Plus: a line in its own menu, called “Try
Plus”. That is the whole of it – no notice across the screen you are working
on, no box on your dashboard, and nothing that counts how often you looked.
The page behind the line has a button that removes the line for good, and it
disappears by itself as soon as Plus is active.
Installation
- Copy the
dt-pm-consentdirectory intowp-content/plugins/. - Activate the plugin.
- Under “DT-PM Consent”, enter every service that sets cookies or transfers data
to third parties. - Check the result: open the site in a private window and use the network tab
to confirm that no request goes to a third party before consent.
Step 4 is not optional. A consent banner whose blocking does not work is worse
than none — it documents that the obligation was known.
FAQ
What exactly does the plugin block, and what does it not?
It blocks nothing on its own. Whatever is not in the service list is not
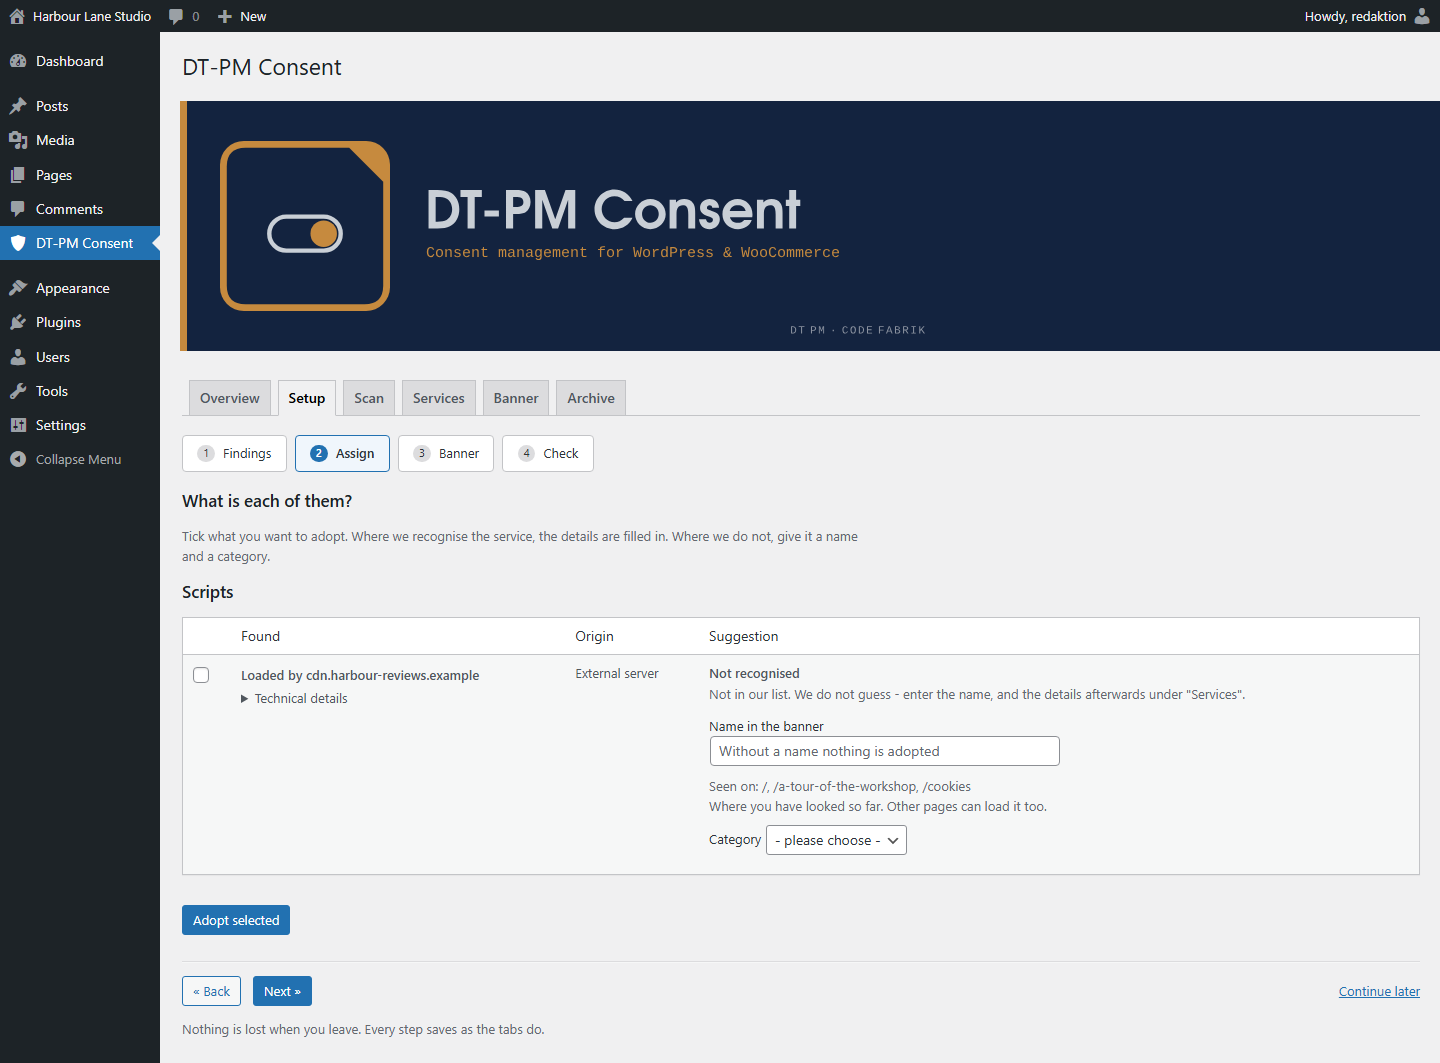
blocked. The setup helper shows the scripts that loaded and suggests an entry
for the ones it recognises — but it adopts nothing without your confirmation.
That is a deliberate decision: a plugin that decides by itself which scripts
on someone else’s website perform tracking would either block too little (and
pretend safety) or too much (and take the site down).
Detection is not complete. It knows a limited number of common services.
An unrecognised script is marked as unknown and presented with empty fields —
the plugin guesses neither provider nor purpose nor storage period. An empty
row you have to fill in is more honest than a filled-in one that is wrong.
The setup helper puts two cases first: external servers and recognised
services. Everything else — WordPress itself, your theme, plugins on your
own server — sits below, collapsed but complete. That is a display decision
and not a legal assessment: a plugin can live on your server and still set
cookies. Go through the second list instead of relying on the first.
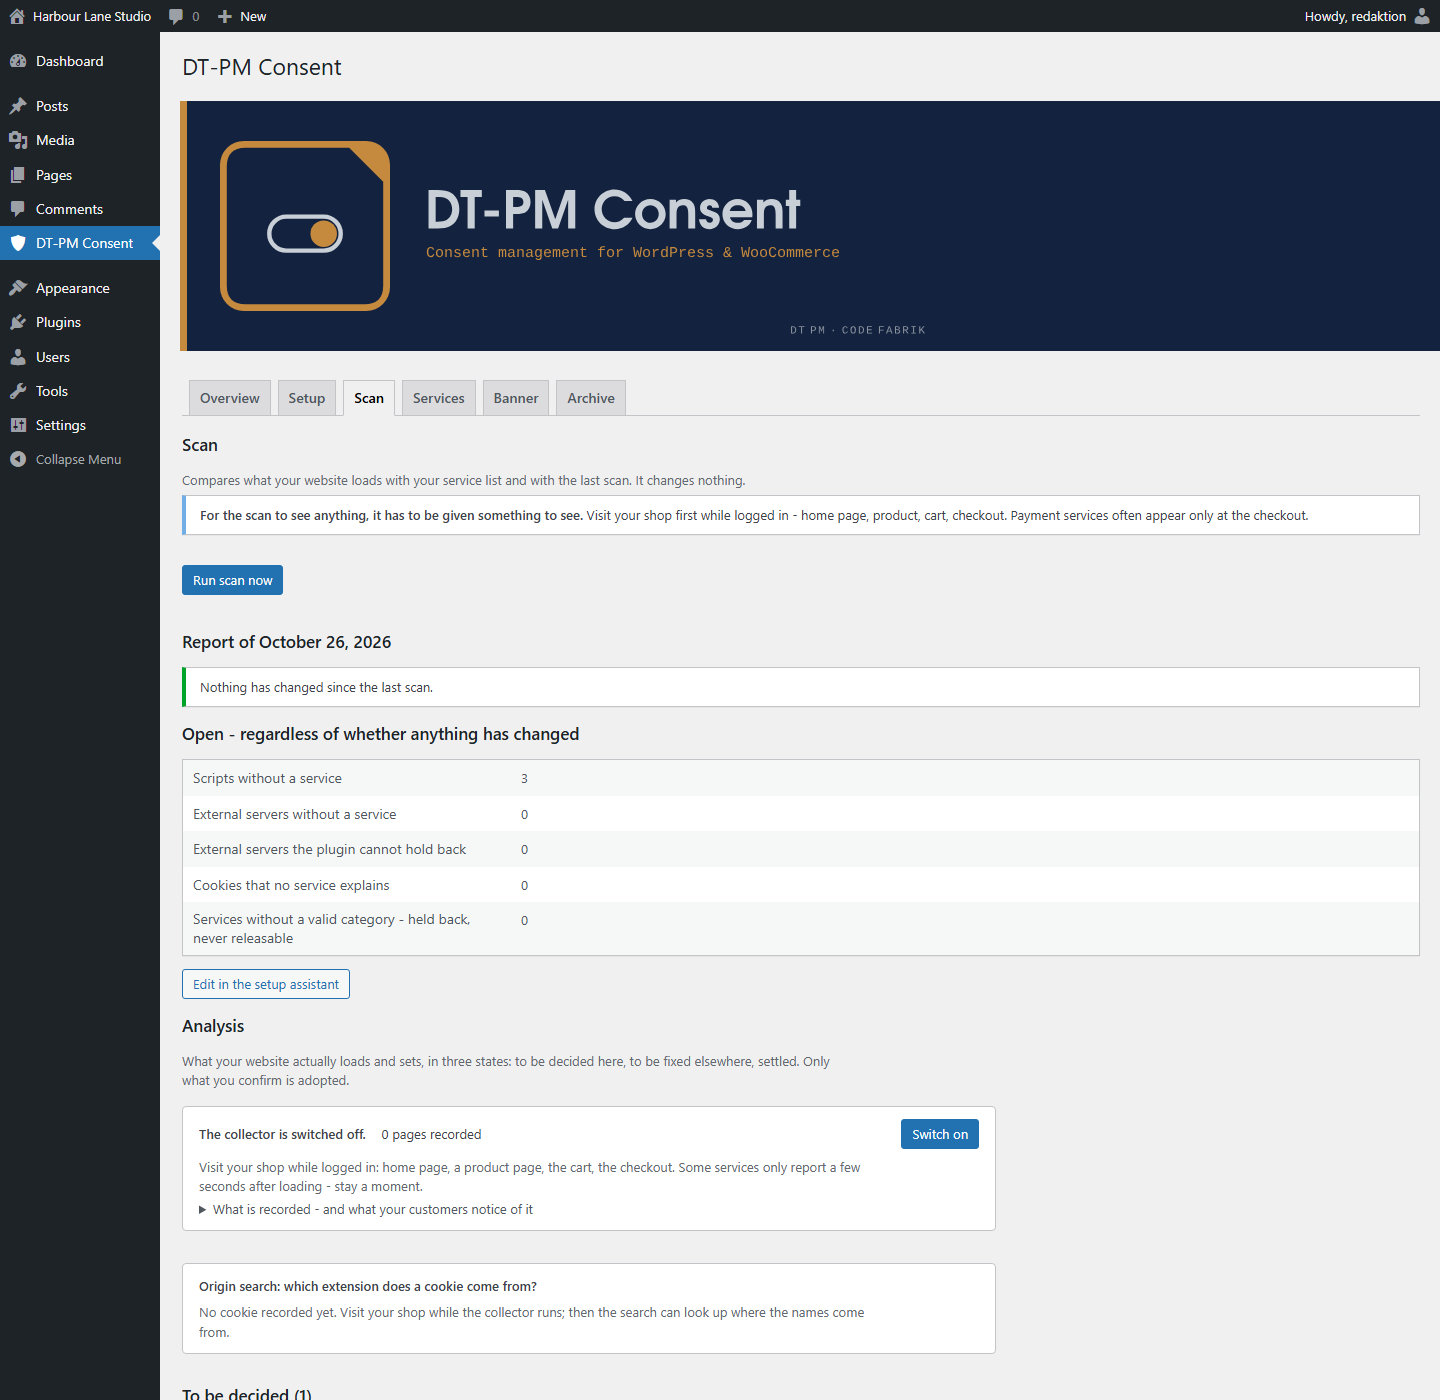
It does not catch scripts written into the markup around the WordPress
API. The collector finds them and tells you they are there — block them
the plugin cannot. You then have to act yourself: remove the integration from
the theme, register it through wp_enqueue_script, or serve the file from
your own server.
It stops nothing that is loaded from inside a stylesheet. An
@import url(‘https://fonts.googleapis.com/…’) or a font in an @font-face
rule keeps loading even when the service is listed as blocked: the plugin can
stop a stylesheet by its ADDRESS, but it does not read what a stylesheet does
inside. Four routes are affected — @import in a <style> block, @import
in an enqueued stylesheet, url() in an @font-face rule, and
background-image.
The setup helper finds and names these cases for every stylesheet enqueued
through WordPress, under “Stylesheets that load from elsewhere”. Acting on
them is up to you: serve the font from your own server, or remove the
reference in the theme. Many themes have a setting for exactly this. A
In detail: blocking applies to scripts registered through
wp_enqueue_script(), to their inline snippets, to snippets entered in the
admin area, and to iframes in post content, text widgets and oEmbed output. A
theme that writes a tracking script directly into a template file is not
covered. Check this after setup with your browser’s developer tools: open the
network tab, load the page without consenting, go through the list.
“Inline snippets” means less than it sounds like, and the difference
matters. It is the snippet WordPress attaches to a registered script — not
any <script> you put into a post. And a script that builds a further script
while the page runs (document.createElement('script')) loads in any case:
the address it assembles exists only in the browser, and the plugin never sees
it. This route is measured and open; it was the same in earlier versions.
It stores no consent of individual visitors. No server-side log, no IP
address, no visitor identifier. The duty to demonstrate consent is met through
the configuration archive: it records which services, purposes and texts were
served at which point in time. The guidance of the German data protection
authorities for providers of digital services states in para. 84 that
demonstrating consent does not require long-lived identifiers.
It is not legal advice. Whether your website meets the requirements with
this plugin depends on which services you use and how you describe them. The
plugin provides the technology; the substantive accuracy of the entries and
the legal assessment remain with you.
How do I find the script handle of a service?
As a rule, no longer by hand: open “DT-PM Consent → Setup helper”, visit your
site’s front end while logged in, and come back. The scripts that loaded are
listed there with their handle and source.
If you do want to look it up yourself: in the page source the handle sits in
the id of the script tag, with -js appended. So
Why does the page reload after a withdrawal?
Because a script that has already run cannot be unloaded again. It keeps
listening for events and would immediately set the deleted cookies anew. Only
a fresh page load, in which the scripts are never activated, actually enforces
the withdrawal.
Why can I not change the label of “Reject all”?
Because supervisory authorities regularly object to banners in which the
rejection has been renamed, hidden or removed altogether. The plugin therefore
does not allow that configuration.
Do I lose the evidence archive when I uninstall?
Yes. Deleting the plugin removes all of its data, the archive included. If you
still need it for an ongoing or expected audit, back it up first.
May I share consent across subdomains of a shared domain?
Only if every subdomain is yours. If you share the parent domain with
other people’s websites — typical for site-builder and hosting offers of the
form yourname.provider.com — please do not switch on “Valid on subdomains”.
The reason is a limit that cannot be closed technically: whoever can set
cookies on a neighbouring subdomain can also write a consent cookie for your
site. Since 0.16.0 the plugin reliably detects that a cookie comes from a
DIFFERENT installation and rejects it. That does not help against deliberate
forgery: the check value sits in the source of every page and can be read from
there. Only a server-side check would be forgery-proof — and that cannot be
reconciled with this plugin’s cache compatibility (see the next question).
With the setting switched off — the default — the problem does not arise.
Does a withdrawal also delete cookies from neighbouring subdomains?
Possibly, yes — and that is a deliberate decision. Many tracking cookies,
_ga from Google Analytics among them, do not sit on your host but on the
parent domain. Without deleting there, a withdrawal would have no effect.
Whether “the parent domain” is yours alone cannot be decided without a
constantly maintained list of every domain suffix in the world.
The trade-off: either the withdrawal fails to delete what it is supposed to
delete, or on a shared domain someone else’s statistics lose a counter. The
first would be a breach of the law, the second an annoyance. Your own consent
cookie has not been affected since 0.16.0 — a neighbour’s decision is no
longer deleted along with it.
Why do I see an empty area instead of a notice when JavaScript is off?
Since 0.19.0 the server only renders a blocked embed harmless; the visible
notice and its button are built by the plugin script in the browser.
The reason is the safety of the blocking itself: as long as the server
assembled the placeholder, it carried over the remaining attributes of the
original embed — and two routes arose along which an embed kept loading inside
the placeholder. The server now outputs no foreign attribute at all.
Without JavaScript nobody can consent anyway; the button had no effect there
before either. Nothing loads without JavaScript — the blocking does not depend
on the script.
Why is an embed blocked although no third party appears in it?
This concerns embeds that carry their content in the srcdoc attribute. If
there is a <script> inside, the plugin blocks — even when no known provider
is recognisable. A script can load anything when it runs, and the plugin
cannot judge what. In case of doubt it does not allow it.
That is the only place where more is blocked on purpose than might be
necessary. A srcdoc without outward references is left alone.
Does the plugin work with caching plugins?
Yes, and that is measured rather than merely argued. The HTML served is
identical for every visitor; the decision about consent is made exclusively in
the browser.
Tested against a real page cache on Apache: a visitor without consent is
served exactly the page that was previously generated and cached for a
consenting visitor — and still loads no script that requires consent.
An upstream proxy cache (Varnish or Cloudflare, say) has not been measured. It
passes on the same HTML, so the statement holds there too — but it is not
demonstrated for it.
Which cookie does DT-PM Consent set itself, and who provides the plugin?
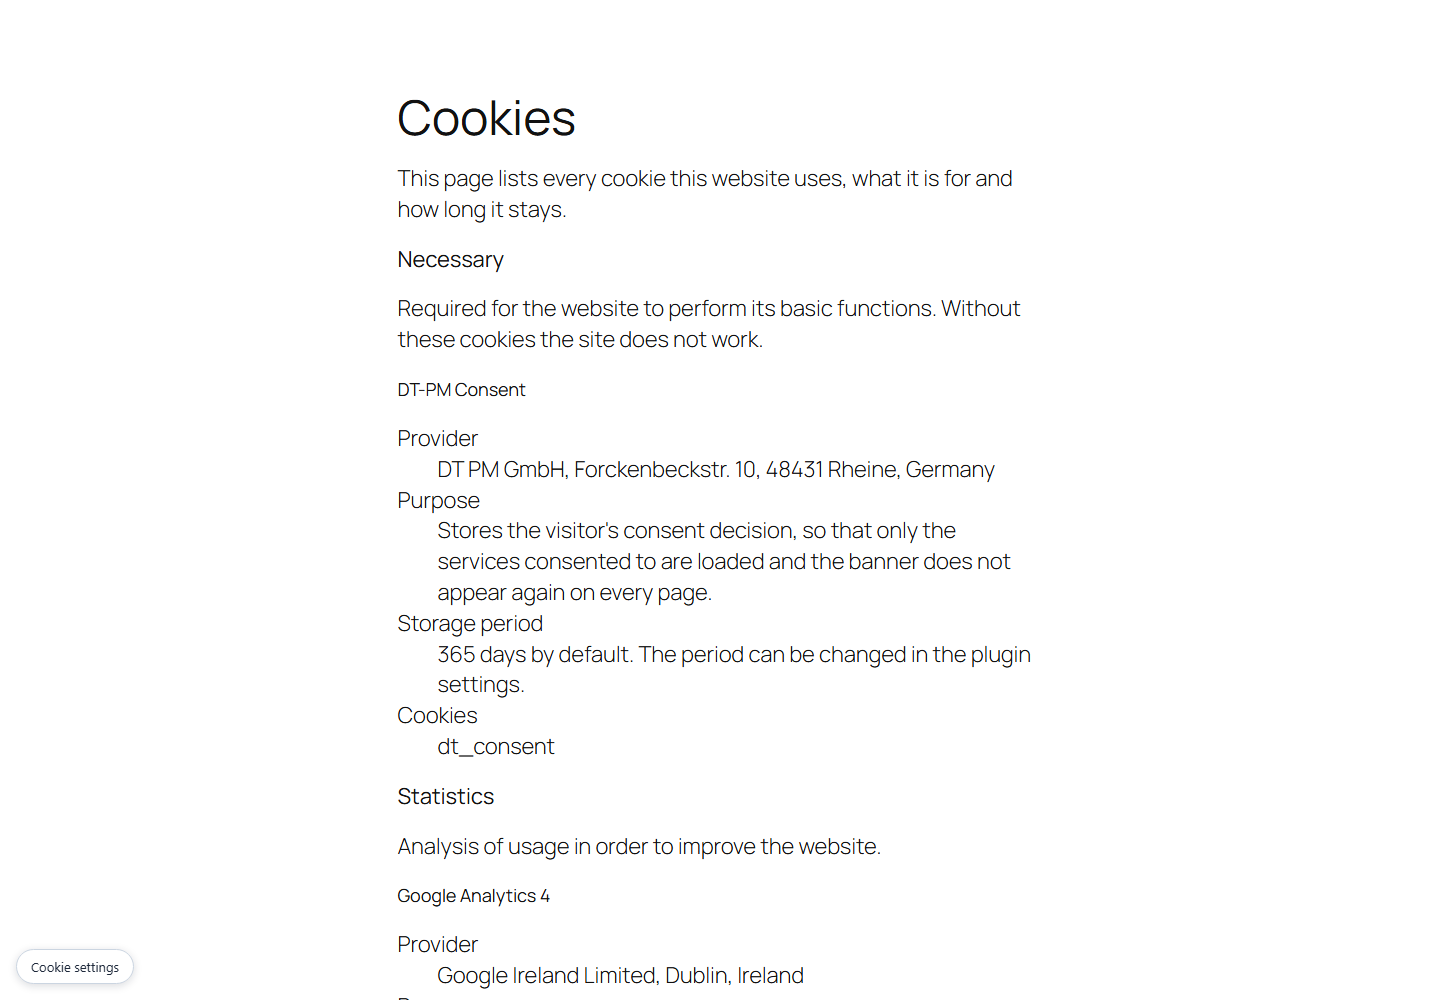
One cookie, named dt_consent. It stores the visitor’s consent decision – which
categories were accepted – together with a fingerprint of the configuration, so
that only the services consented to are loaded and the banner does not appear
again on every page. When the service or purpose list changes in substance, the
fingerprint no longer matches and the banner appears again.
It is kept for 365 days by default; the period can be changed on the “Banner”
tab. The plugin sets it in the visitor’s browser and sends it to no one: there
is no transfer to a third party and none to a third country.
DT-PM Consent is provided by DT PM GmbH, Forckenbeckstr. 10, 48431 Rheine, Germany.
Can I extend the plugin from my own code?
Yes, and without touching its files. Four hooks are documented and will not
change their names:
dt_consent_service_catalogue(filter) adds your own service to the built-in
catalogue, so the plugin recognises it like any other.dt_consent_scan_report(action) hands you every finished scan report, for
your own monitoring or ticket system.dt_consent_configuration_archived(action) hands you every configuration
that went into the evidence archive, for your own records.dt_consent_banner_classes(filter) adds a CSS class to the banner, so a
theme can style it without copying markup.
The content of the banner is deliberately not filterable: both buttons, the
purposes and their order are what this software is measured against.
How do I style the banner with my own CSS?
Add your rules to your theme or to a custom-CSS field. The banner uses the
classes dtc-banner (the overlay), dtc-banner__inner (the box) and
dtc-button (both level-one buttons). The filter
dt_consent_banner_classes adds a class of your own to the banner, so you
can target your site without copying any markup.
Since 1.0.10 a plain class is no longer enough. The plugin’s own rules
repeat their class four times, so
.dtc-button { background: #123456; }
will not take effect. Use the same specificity:
.dtc-button.dtc-button.dtc-button.dtc-button { background: #123456; }
The reason is measured, not theoretical: some themes raise the specificity of
their own button rules above a plain class, and on those themes none of this
plugin’s buttons showed the colour the plugin sets – not the two level-one
buttons, not the save button, not the revoke entry that sits on every page.
Repeating the class is what wins against that pattern. It is not a guarantee
against every theme, and a theme using !important still wins.
Whatever you change, change it for both level-one buttons. “Accept all”
and “Reject all” share one class on purpose. Supervisory authorities treat a
prominent accept button next to a quiet reject button as unlawful influence
(DSK guidance, para. 60), and this plugin is built so that there is no place
where only one of the two can be coloured. A rule that singles one of them
out defeats that, and it is your installation that has to answer for it.
The save button (dtc-button--quiet) is deliberately quieter. It confirms a
selection you have already made; it is not a third alternative to accepting
and rejecting, so the equivalence requirement does not apply to it.
Why does the cookie declaration name DT PM GmbH?
Because the plugin sets the dt_consent cookie on your site, and a visitor is
entitled to know who is behind a cookie (Art. 13 GDPR). The cookie declaration
therefore lists DT-PM Consent like any other service, and the provider line names
the company that provides the plugin.
This is information about a cookie, not a credit. It is plain text: no link, no
logo, no promotional wording. It appears only where you place the cookie
declaration (the [dt_consent_cookies] shortcode or the block) – never in the
banner, the footer or anywhere else on your pages. It disappears when the
plugin is deactivated, because then the cookie is no longer set.
Screenshots


Changelog
Older entries live in changelog.txt in the plugin folder. WordPress.org cuts
this section off at 5,000 characters, and a cut-off changelog looks like one
that ends.
1.2.1
The paid edition now has one line in the menu, and nothing else. It is
called “Try Plus”, and the page behind it says what Plus adds – and, first,
what this plugin does without it.
- One button on that page removes the line for good. It also disappears on
its own as soon as Plus is active: whoever paid sees no advertising. - Still no request of its own. The link goes to our page and carries
nothing that would say which installation it came from – no key, no version,
no parameter at all. - No notice over your screen and no box on your dashboard. Both would be
allowed; neither fits a plugin whose point is that it stays out of the way.
1.1.8
Your banner can now speak your language. Five of its texts were always
yours to write. The rest – the two buttons, the categories, the details per
service – comes from a translation file, and this edition carries none: the
plugin directory builds and delivers translations itself, and it does so once
a language reaches 90 % of all texts. Below that, nothing arrives, and the
banner stays English.
Under “Banner” there is now a table of the languages we have translated. You
download the file for yours, upload it there, and the plugin puts it where
WordPress reads translations from – no FTP and no folder names, as long as your
hosting lets the plugin write there. If it does not, the plugin says so and
names the folder, so you can copy the file yourself.
- The plugin still makes no request of its own. You fetch the file; it
does not. Should WordPress.org deliver a translation later, that one
replaces yours – it covers more than the banner. - It only accepts a compiled translation file that belongs to this plugin. The
name of the file decides nothing; its content does. Every reason to turn a
file away on its content has its own test, and so has every one of the seven
translations we ship: they go through the same check the upload does. - Correction to 1.1.6: the changelog there mentions a corrected German
sentence in the block editor. That file is not in the package – the free
edition has carried no translations since 1.1.4. The correction reaches you
with a language pack, not with the update.
1.1.6
The plugin page, rewritten and cut to a third. What this plugin is, and
what it refuses to do, now stands at the top instead of after four
paragraphs. No limitation was dropped: the detail about what exactly is
blocked – and what cannot be – moved into the FAQ, where you look for it.
- One German sentence in the block editor changed. The cookie declaration
block describes itself differently now; its translation file had been out
of date since the wording was reworked in 1.1.5.
No code changed in this version, and no setting of yours is touched.
1.1.5
Ten notices rewritten so that you can act on them. They used to say what
the plugin was missing. They now say what it costs you, and where to put it
right.
- A service that is listed but not stopped. The notice begins with the
part that matters: your banner asks permission for the service, but the
answer has no effect – it loads even when the visitor says no. It then says
what the plugin needs in order to recognise the service, in everyday words,
and where to find it. The block that holds those fields now opens by
itself while the notice is showing; before, it stayed shut in exactly the
case where you needed it. - A category that no longer exists. A name entered twice. Cookies that no
service claims. Style files that load from somewhere else. Same
treatment: what it means for your site first, the field or the page to fix
it in last – and no term that only a developer knows. - Nothing you have configured is touched, and no check decides differently
than before. What changed is the wording, plus the one block that now opens
on its own.