


Description
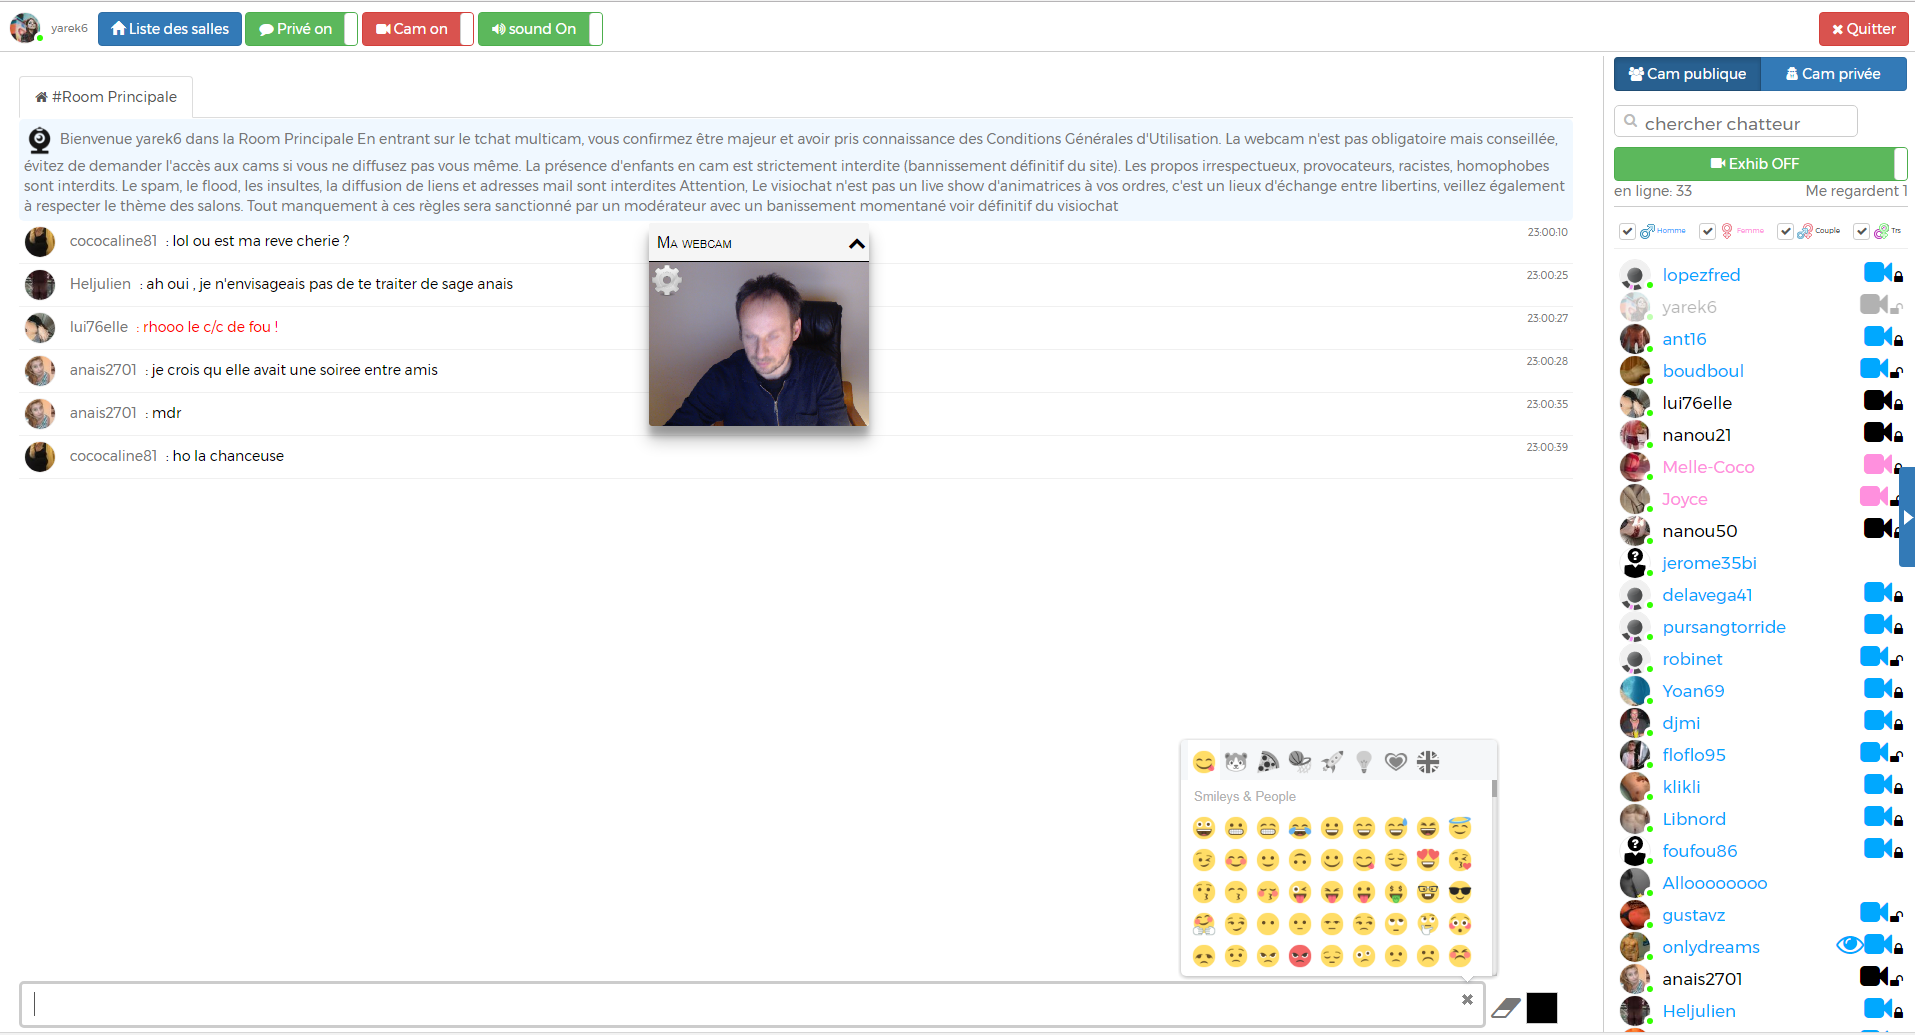
HTML5 Chat allows you to quickly add a live audio and video chat to any WordPress page or post.
The plugin embeds the HTML5-based chat service from html5-chat.com, without requiring any technical configuration.
Once activated, you can insert the chat anywhere using a simple shortcode.
Key features:
– Live audio & video chat (HTML5)
– Simple shortcode integration
– Customizable width & height
– Fullscreen mode support
– Admin moderation tools
– CSS customization via admin panel
– Works on desktop and mobile browsers
After activation, your chat access credentials are automatically sent to your WordPress admin email.
Security note:
Version 1.07 includes a security fix for a stored Cross-Site Scripting (XSS) vulnerability in shortcode attributes (CVE-2024-12451).
Credit: Peter Thaleikis / Wordfence.
Support
For questions or assistance, please contact:
contact@proxymis.com
Installation
- Install and activate the plugin
- Create or edit a page/post
- Insert the shortcode:
[HTML5CHAT width=100% height=640px] - Configure the chat appearance and behavior using the “Configure the chat here” link in your WordPress admin
- Optional: enable fullscreen mode using:
[HTML5CHAT width=100% height=fullscreen]
FAQ
How do I change the chat width and height?
Edit the shortcode attributes:
[HTML5CHAT width=100% height=640px]
Supported units:
%, px, vw, vh, rem, em
How do I enable fullscreen chat?
Use:
[HTML5CHAT width=100% height=fullscreen]
How can I moderate the chat?
If you are logged in as a WordPress administrator, you are automatically the chat administrator.
Can I customize the look & feel?
Yes. The configuration panel allows you to inject custom CSS and adjust the chat behavior.
Screenshots


Changelog
1.08
- Minor improvements and compatibility updates
1.07
- Security: Fixed stored XSS in shortcode attributes (CVE-2024-12451)
- Hardening: Sanitized and validated shortcode dimensions
- Escaped output URLs
- Credit: Peter Thaleikis / Wordfence