

Description
Protect your WordPress website against brute force attacks, bot attacks, and unauthorized login attempts with one of the most trusted login security plugins for WordPress.
Limit Login Attempts Security strengthens your WordPress login security by limiting failed login attempts, blocking malicious IPs, securing wp-login.php, protecting XML-RPC, and adding powerful firewall and 2FA protection without slowing down your website.
Trusted by 2 million WordPress websites, Limit Login Attempts Security is designed specifically to protect the most targeted part of your website: the login page.
Why Use Limit Login Attempts Security?
By default, WordPress allows unlimited login attempts. This creates a major security vulnerability where bots and attackers can repeatedly guess usernames and passwords until they gain access. This is especially important in the age of AI, where attackers now have access to faster and more sophisticated tools than ever before.
Limit Login Attempts Security helps stop:
- Brute force attacks
- Bot login attacks
- Credential stuffing attacks
- XML-RPC attacks
- Unauthorized login attempts
- WooCommerce login abuse
- Malicious IP access attempts
The plugin automatically blocks excessive login attempts and locks out suspicious IP addresses and usernames before attackers can gain access.
Features Included in the Free Version
Login Security & Brute Force Protection
- Limit login attempts by IP address and username
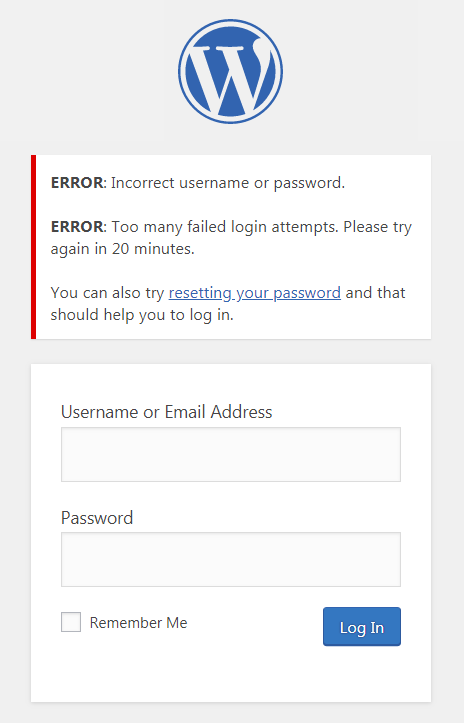
- Automatically lock out suspicious login activity
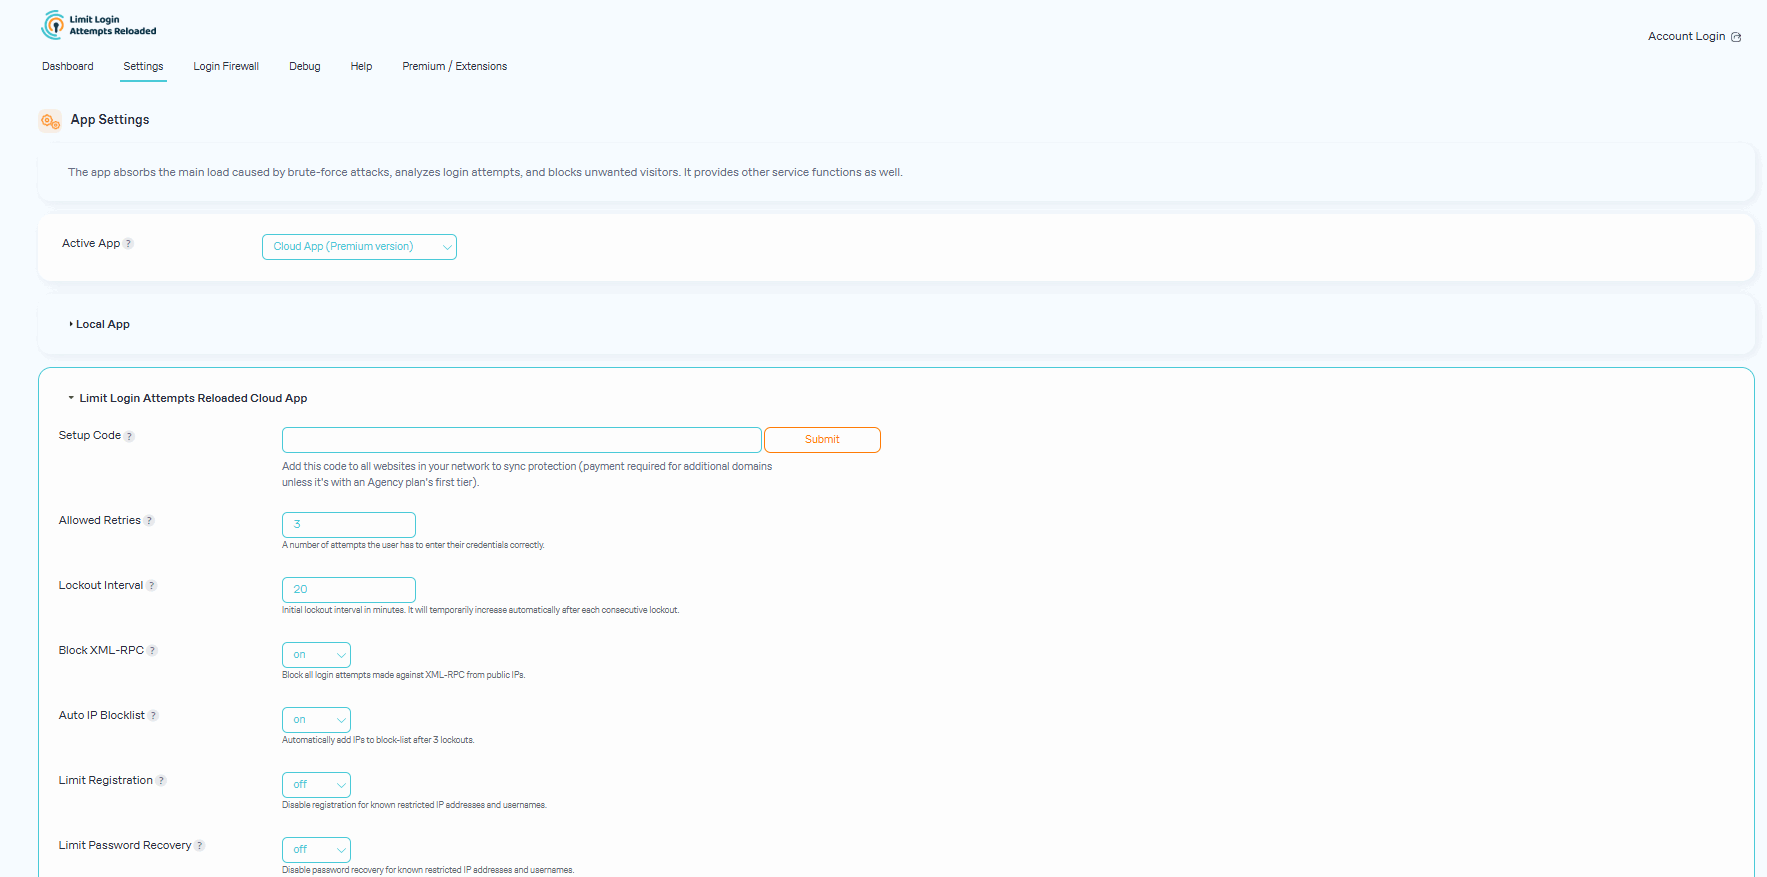
- Adjustable lockout duration and retry limits
- Protect wp-login.php from automated attacks
- Prevent brute force login attacks
2FA / Multi-Factor Authentication (MFA)
- Built-in two-factor authentication (2FA)
- Add an additional layer of login protection
- Improve WordPress account security
- Secure administrator and user logins
Firewall & Bot Protection
- Block malicious login requests
- Detect suspicious login behavior
- Reduce bot-based login attacks
- Lightweight firewall-focused login protection
WooCommerce & Plugin Compatibility
Protects:
- WooCommerce login pages
- XML-RPC login requests
- Custom login pages
- WordPress multisite installations
Compatible With:
- Wordfence
- Sucuri
- Ultimate Member
- MemberPress
- WPS Hide Login
- Cloudflare and reverse proxy setups
Login Monitoring & Notifications
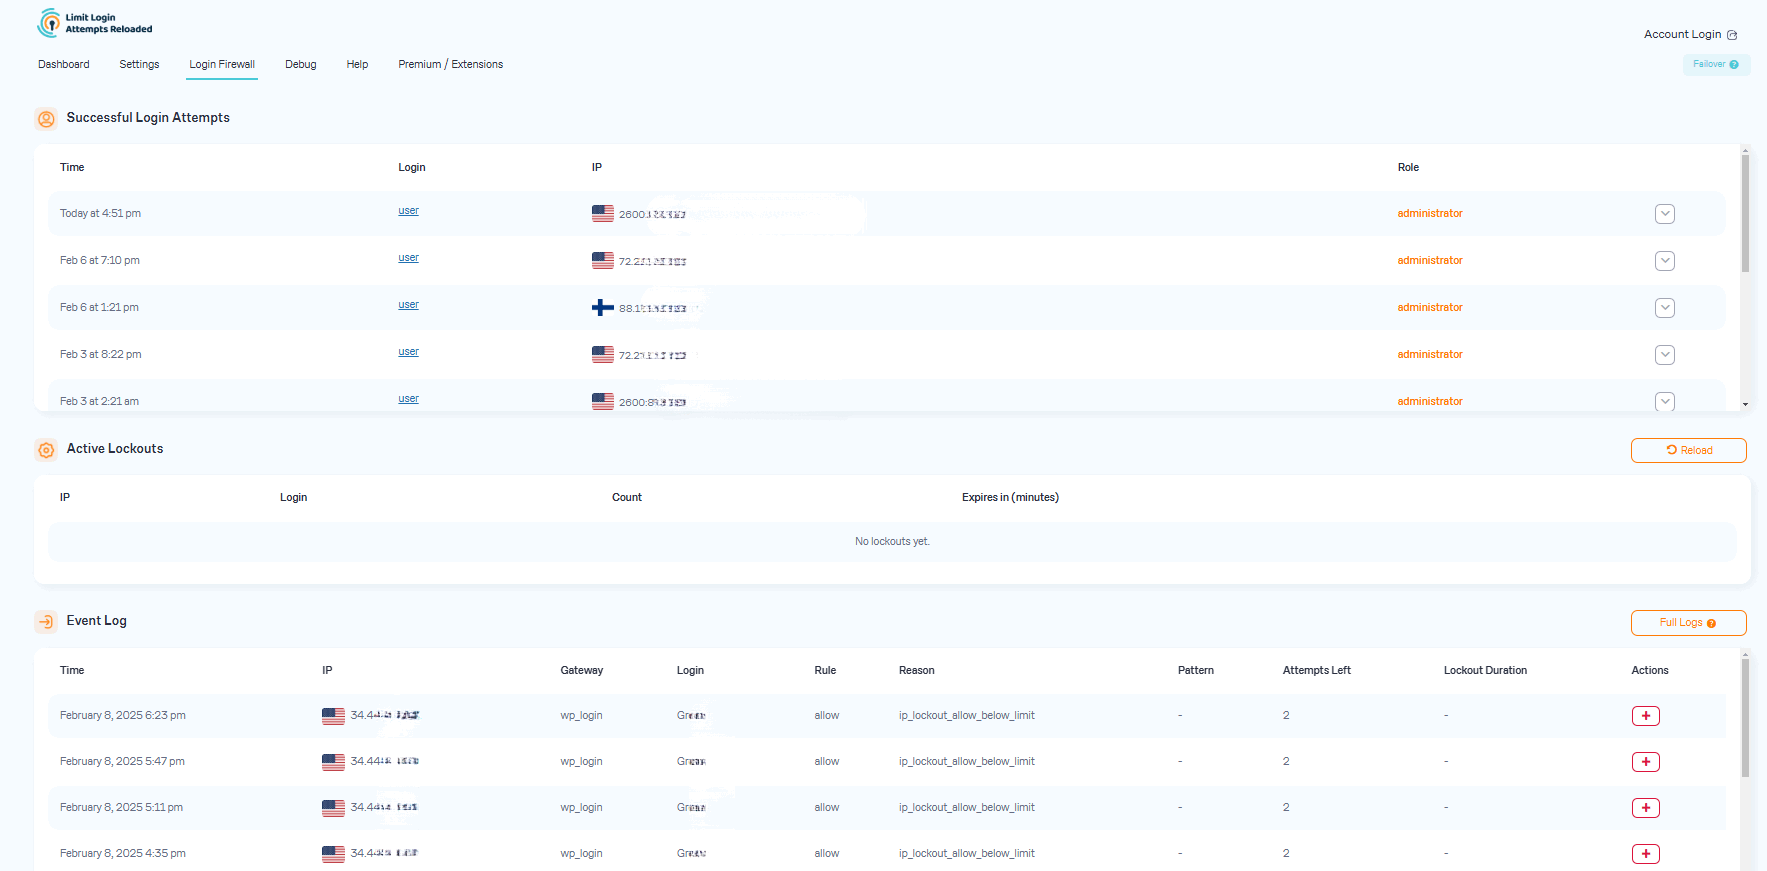
- Failed login attempt logs
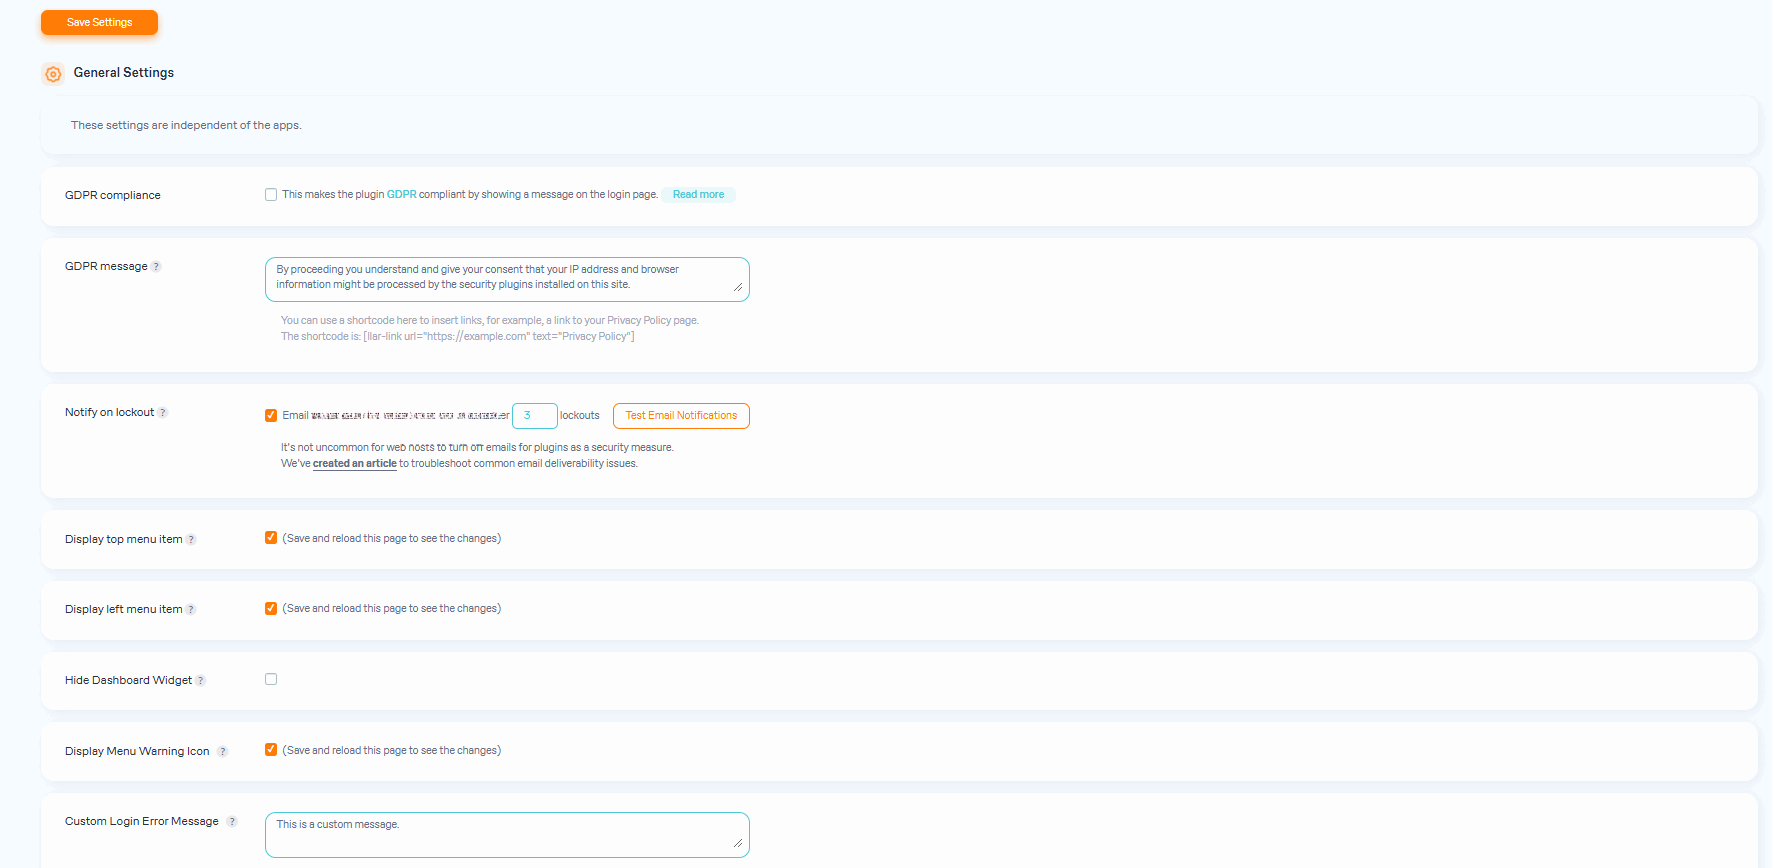
- Lockout email notifications
- Denied attempt tracking
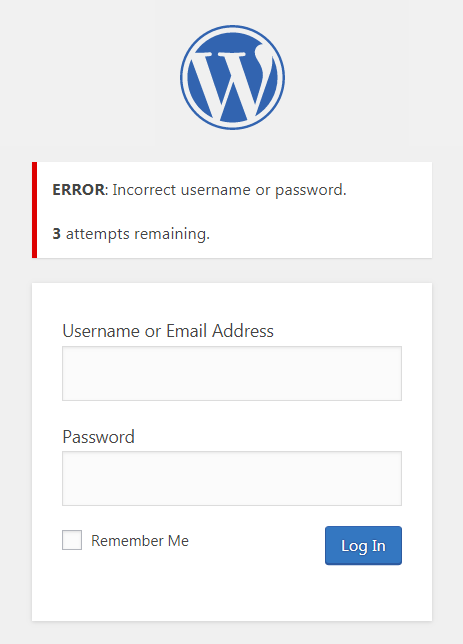
- Login retry visibility for users
Access Controls
- IP safelist and denylist support
- Username safelist and denylist support
- IPv6 range support
- Custom IP origin configuration
Premium Features (Start Your Free 7 Day Trial)
Upgrade to Limit Login Attempts Security Premium to extend protection with cloud-based login security and advanced attack prevention.
Advanced Cloud Protection
- Real-time malicious IP intelligence
- Global denylist protection
- Synchronized lockouts across websites
- Auto IP denylist generation
- Cloud-based login attack mitigation
Enhanced Performance Protection
- Offload excessive failed login requests from your server
- Reduce server strain during attacks
- Improve stability under heavy attack conditions
Advanced Security Features
- Country-based login blocking
- Enhanced throttling and lockout escalation
- Registration page protection
- Successful login tracking
- Enhanced lockout analytics and geolocation data
Multi-Site & Team Features
- Shared safelist and denylist syncing
- Shared lockout protection between domains
- Cloud backups of IP security data
- CSV exports of login and IP activity
Premium Support
- Access to security-focused support specialists
- Faster troubleshooting and assistance
Lightweight Security Built for WordPress
Unlike many large security suites, Limit Login Attempts Security focuses specifically on login security and brute force protection.
This means:
- Faster performance
- Less server overhead
- Easier configuration
- Strong protection without unnecessary bloat
Protect More Than Just wp-login.php
Limit Login Attempts Security secures:
- wp-login.php
- XML-RPC
- WooCommerce logins
- Custom login forms
- Registration pages
- Multisite logins
Trusted by Millions of WordPress Websites
Limit Login Attempts Security is one of the most widely used WordPress login security plugins and has helped protect millions of websites from brute force attacks and malicious login activity.
Whether you run:
- A personal blog
- WooCommerce store
- Membership website
- Agency
- Business website
- Enterprise WordPress network
Limit Login Attempts Security helps secure your login experience with modern WordPress login protection.
Upgrading from the Original Limit Login Attempts Plugin?
Switching is easy:
- Remove the old Limit Login Attempts plugin
- Install Limit Login Attempts Security
- Your settings will remain intact
Translation Support
Currently translated into multiple languages including:
- Spanish
- French
- German
- Dutch
- Turkish
- Swedish
- Russian
- Romanian
- Chinese (Traditional)
- Brazilian Portuguese
- And more
Secure Your WordPress Login Today
Install Limit Login Attempts Security and protect your WordPress website with:
- Login security
- Two-Factor Authentication (2FA)
- Brute force protection
- Firewall security
- Bot protection
- XML-RPC protection
- WooCommerce login protection
Without slowing down your website.
FAQ
What do I do if all users get blocked?
If you are using contemporary hosting, it’s likely your site uses a proxy domain service like CloudFlare, Sucuri, Nginx, etc. They replace your user’s IP address with their own. If the server where your site runs is not configured properly (this happens a lot) all users will get the same IP address. This also applies to bots and hackers. Therefore, locking one user will lead to locking everybody else out. If the plugin is not using our Cloud App, this can be adjusted using the Trusted IP Origin setting. The cloud service intelligently recognizes the non-standard IP origins and handles them correctly, even if your hosting provider does not.
How do I know if I’m under attack?
An easy way to check if the attack is legitimate is to copy the IP address from the lockout notification and check its location using a IP locator tool. If the location is not somewhere you recognize and you have received several failed login attempts, then you are likely being attacked. You might notice dozens or hundreds of IPs each day. Visit our website to learn how can you prevent brute force attacks on your website.
How can I tell that the premium plugin is working?
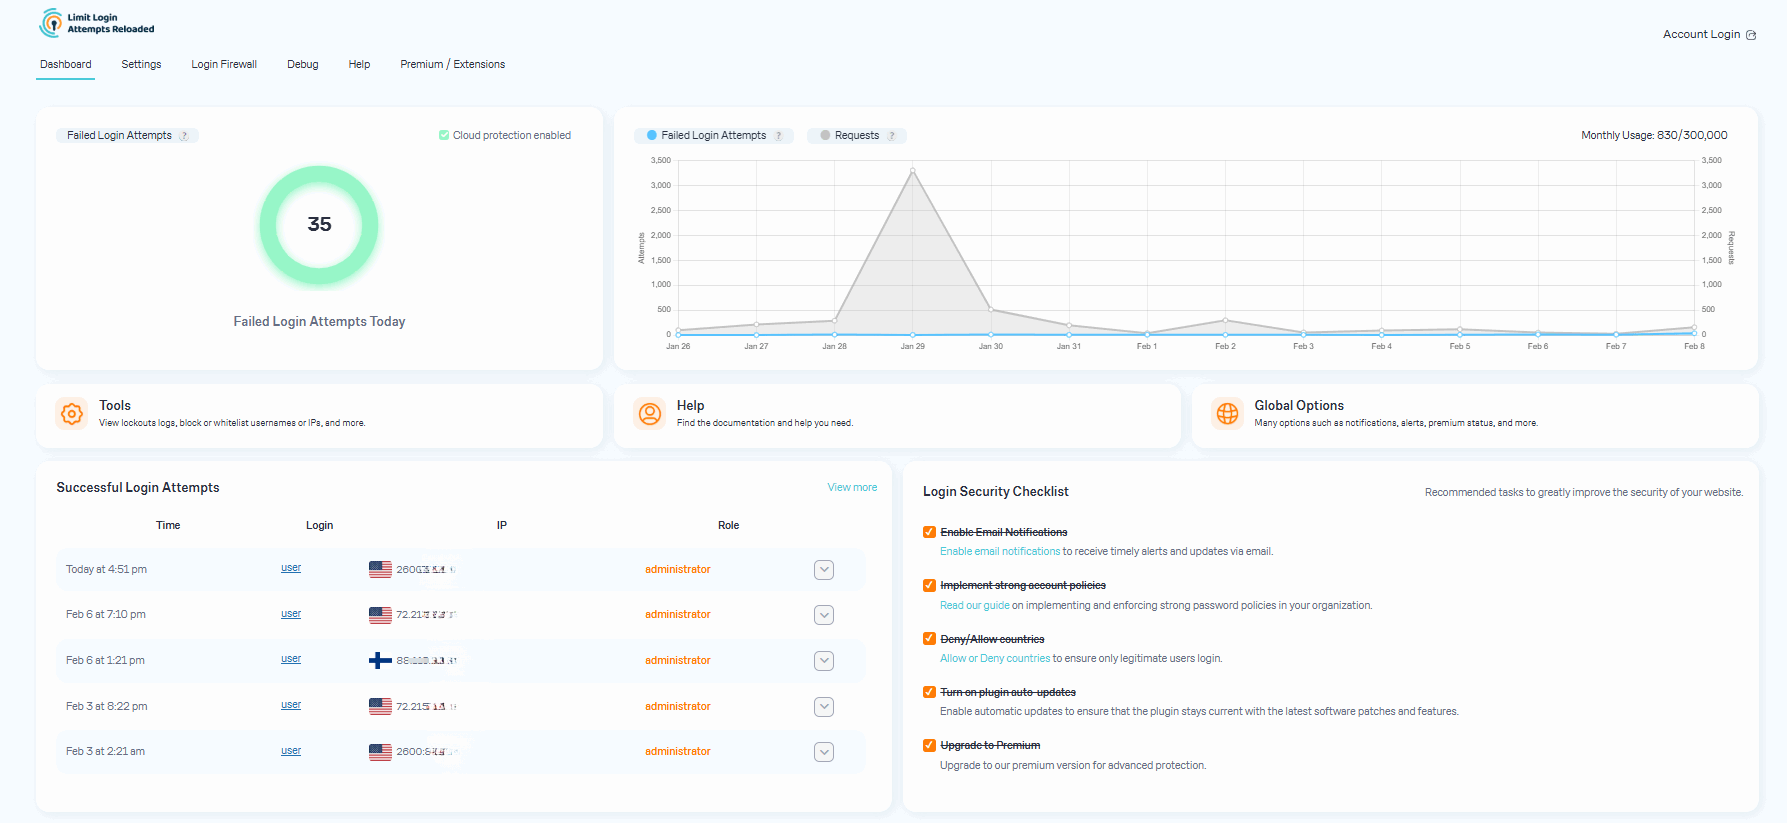
After you upgrade to our premium version, you will see a new dashboard in your WordPress admin that shows all attacks that will now relay through our cloud service. On the graph, you’ll see requests and failed login attempts. Each request will represent the cloud app validating an IP, which also includes denied logins.
In some cases, you may notice an increase in speed and efficiency with your website. Also, a reduction in lockout notifications via email.
Could these failed login attempts be fake?
Some users find it hard to believe that they could experience numerous unsuccessful login attempts, particularly when their site has just been established or has minimal human traffic. The plugin is not responsible for generating these failed login attempts. Newly created websites are frequently hosted on shared IP addresses, making it easy for hackers to discover them. Additionally, newly registered domain names are often crawled soon after creation, rendering a WordPress website susceptible to attacks. Such websites are attractive targets as security is not a primary concern for their owners. We’ve created an article that delves deeper into the issue of fake login attempts in WordPress.
What happens if my site exceeds the request limits in the plan?
The premium plan’s resource limits start from 100,000 requests per month, which should accept almost any heavy brute-force attack. We monitor all of our sites and will alert the user if it appears they are going over their limits. If limits are reached, we will suggest to the user upgrading to the next plan. If you are using the free version, the load caused by brute force attacks will be absorbed by your current hosting bandwidth, which could cause your hosting costs to increase.
What URLs are being attacked and protected?
The URLs being protected are your login page (wp-login.php, wp-admin), xmlrpc.php, WooCommerce login page, and any custom login page you have that uses regular WordPress login hooks.
Why is Limit Login Attempts Security more popular than other brute-force protection plugins?
Our main focus is protecting your site from brute force attacks. This allows our plugin to be very lean and effective. It doesn’t require a lot of your web hosting resources and keeps your site well-protected. More importantly, it does all of this automatically as our service learns on its own about each IP it encounters. In contrast, a firewall would require manual blocking of IPs.
What to do when an admin gets blocked?
Open the site from another IP. You can do this from your cell phone, or using Opera browser and enabling free VPN there. You can also try turning off your router for a few minutes and then see if you get a different IP address. These will work if your hosting server is configured correctly. If that doesn’t work, connect to the site using FTP or your hosting control panel file manager. Navigate to wp-content/plugins/ and rename the limit-login-attempts-reloaded folder. Log in to the site then rename that folder back and whitelist your IP. By upgrading to our premium app, you will have the unlocking functionality right from the cloud so you’ll never have to deal with this issue.
What settings should I use In the plugin?
The settings are explained within the plugin in great detail. If you are unsure, use the default settings as they are the recommended ones.
Can I share the safelist/denylist throughout all of my sites?
By default, you will need to copy and paste the lists to each site manually. For the premium service, sites are grouped within the same private cloud account. Each site within that group can be configured if it shares its lockouts and access lists with other group members. The setting is located in the plugin’s interface. The default options are recommended.
Screenshots
Changelog
3.4.4
- A failed two-factor verification email is now written to the error log with the mail error, so the failure is no longer only an HTTP 500.
- Passing a WP_Error to the failed-login hook no longer crashes PHP 8. The attempt is still counted.
- Added an Extensions tab with easy installation of recommended plugins.
- The PHP vulnerability notice no longer treats a vendor suffix (such as -nts or -ubuntu) on an already patched version as vulnerable. Pre-release builds (dev, alpha, beta, RC) still show the notice.
3.4.3
- Security: IPv6 addresses in the same /64 now share one lockout, so changing the address ending no longer bypasses the login limit. Thanks to Drakon Tech Solutions SLU for the report.
- Shortened onboarding to two steps.
3.4.2
- Security: blocked a server-side request forgery (SSRF) in the app setup feature. The setup destination is validated before fetching, and redirects are checked again. Thanks to Viktor Heiduck for the report.
3.4.1
- Two-factor authentication now applies to XML-RPC logins as well as the login form. Thanks to Qi Qin for the report.
- An invalid X-Forwarded-For header no longer stops the two-factor check. Thanks to Naoki Kawahigashi for the report.
- Added an admin notice when the reported PHP version is below the upstream release that fixes critical PHP vulnerabilities. The notice explains that a host or distribution may already have patched PHP without changing the version number, and tells admins to dismiss it instead of opening a support ticket in that case.
3.4.0
- Added a red dot to the admin menu and admin bar when Micro Cloud requests are exhausted.
- Introduced a 7-day free trial with consent-based activation across the plugin.
Earlier versions
For the changelog of earlier versions, please refer to the changelog.txt file.